5 Technology Decisions Healthcare Organizations Should Get Right Before They Scale
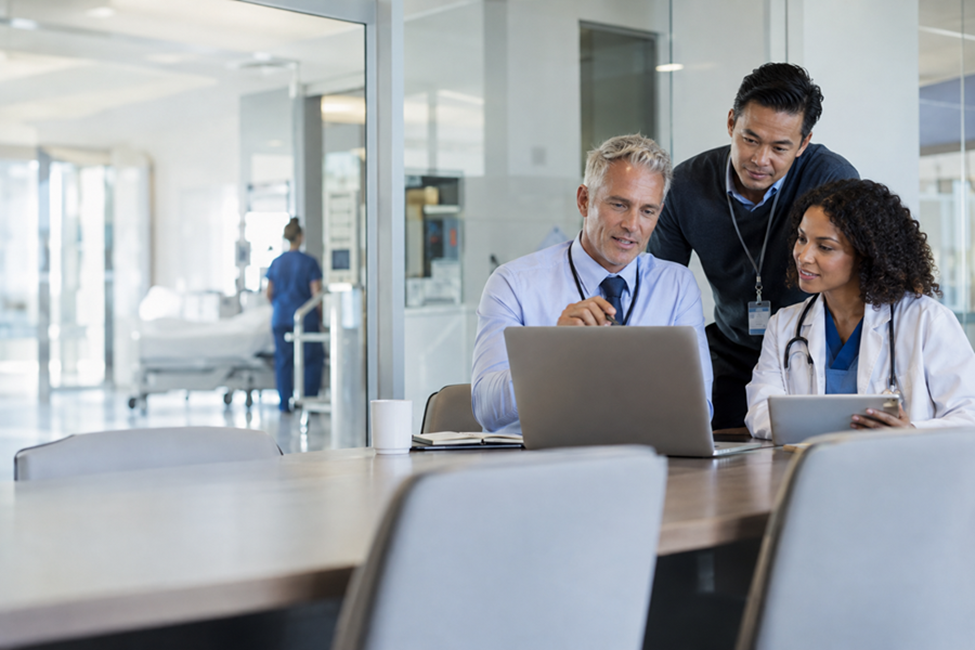
Growth creates new opportunities for healthcare organizations, but it also places greater demands on the technology supporting daily operations. More employees, devices, locations, applications, and patient interactions can expose weaknesses that were manageable when an organization was smaller.
The challenge is not simply acquiring more technology. Healthcare leaders need a technology environment that remains reliable, secure, manageable, and compatible with the way clinicians and administrative teams actually work.
Before expanding operations, opening another location, or adding new digital services, healthcare organizations should examine five technology decisions that can become increasingly difficult to correct later.
1. Build Infrastructure for Tomorrow’s Workload
Technology infrastructure that meets today’s needs may not be sufficient after adding providers, workstations, connected devices, cloud applications, or another facility.
Healthcare organizations should therefore consider scalability before capacity becomes a problem. Networks, storage, cloud resources, connectivity, and device management should be able to accommodate reasonable growth without requiring the entire environment to be rebuilt every time demand increases.
Redundancy deserves attention as well. A system may perform well during normal operations but still create significant disruption if a critical component fails. Planning for backup connectivity, protected data, recovery procedures, and alternative ways to access essential systems can make the technology environment more resilient.
The goal is not to purchase unnecessary capacity in advance. It is to avoid creating architectural limitations that make ordinary growth unusually expensive or disruptive.
2. Build Security and Compliance Into the Foundation
Security becomes harder to manage when it is added after systems, users, vendors, and workflows are already established.
For organizations subject to HIPAA, protecting electronic protected health information involves administrative, physical, and technical safeguards. Risk analysis and ongoing risk management are also important parts of the Security Rule rather than one-time activities.
That makes security architecture an operational consideration, not simply an IT checklist.
Access permissions, authentication, device management, network protection, monitoring, data protection, and documented procedures should be considered when systems are introduced or changed. Organizations can also use structured approaches such as the NIST Cybersecurity Framework to organize and communicate cybersecurity risk management efforts.
When evaluating Healthcare Technology Solutions, healthcare leaders should therefore look beyond individual products and consider how infrastructure, cybersecurity, compliance requirements, communications, and ongoing support work together as one environment.
That broader perspective can help prevent a situation in which every individual system appears acceptable but the connections between those systems introduce operational or security gaps.
3. Make Technology Fit Clinical Workflows
A secure system is not automatically an effective system.
Technology should support the people using it instead of introducing unnecessary steps into patient care and administrative work. Before adopting a new platform or redesigning infrastructure, organizations should understand how information moves through the practice.
Where do clinicians access records? Which employees need remote access? How are patients communicating with staff? Which applications must exchange information? What happens when a provider moves between an examination room, office, and remote location?
These questions can reveal requirements that may be overlooked when technology decisions are made from specifications alone.
Healthcare interoperability is particularly relevant because the ability to exchange and use electronic health information can support coordinated, patient-centered care. Technology planning should therefore consider connections between systems rather than treating every application as an isolated purchase.
Testing changes with the people who perform the work can also expose workflow problems before they become organization-wide frustrations.
4. Plan for Downtime Before Downtime Happens
Healthcare organizations depend on technology for scheduling, documentation, communication, billing, records access, and many other routine activities.
As dependence increases, so does the importance of answering a simple question: what happens when a critical system becomes unavailable?
A practical continuity plan should identify essential systems, determine which operations must be restored first, establish responsibilities, and document alternative procedures where appropriate.
Backups are important, but simply having backup data is not the same as knowing that operations can be restored effectively. Organizations should understand what is being protected, how frequently protection occurs, who can initiate recovery, and how restoration procedures will be tested.
Continuity planning should also evolve whenever important systems, facilities, vendors, or workflows change.
5. Decide Who Owns the Technology Strategy
One of the easiest technology problems to overlook is unclear accountability.
Different vendors may manage internet connectivity, applications, phones, security products, cloud services, hardware, or specialized clinical systems. When responsibilities overlap, problems can turn into prolonged conversations about which provider owns the issue.
Healthcare organizations should establish clear ownership for technology planning, security coordination, vendor management, support, documentation, and long-term improvements.
That does not necessarily mean every responsibility must be handled internally. The important point is that someone needs visibility across the technology environment and responsibility for connecting technology decisions to operational priorities.
Regular technology reviews can then examine emerging risks, aging infrastructure, support trends, upcoming business changes, and investments that should be planned before they become emergencies.
Conclusion
Healthcare growth should not require choosing between better technology, reliable operations, practical workflows, and strong security.
Organizations that make infrastructure, security, workflow, continuity, and accountability decisions early are better positioned to adapt as their needs change. Instead of evaluating technology one product or problem at a time, healthcare leaders can benefit from viewing the entire environment as an interconnected operational foundation.
That approach makes technology planning less about reacting to the next issue and more about creating systems that can continue supporting the organization as patient needs, staff requirements, digital services, and business priorities evolve.
Leave a reply
You must be logged in to post a comment.